
Hackers from the group ShinyHunters claim to have stolen personal data of “all” FBI employees and applicants, according to a report published Tuesday by 404 Media.
The group, which was also behind a breach that disrupted software used by 9,000 schools during final exams in May, reportedly gained access to the FBI’s recruitment site via an exploit in Oracle’s PeopleSoft product. ShinyHunters says it now has sensitive data on individuals who applied for FBI jobs as well as current employees, according to 404 Media. ShinyHunters couldn’t be reached for comment.
As of Wednesday afternoon, the apply.fbijobs.gov site shows a maintenance page reading, “We’re sniffing out site updates for you!” The main FBI Jobs home page serves up a “503 Service Temporarily Unavailable” error page. The bureau’s page highlighting eligibility for new applicants is live with a “System Unavailable” banner reading, “Apply.fbijobs.gov and the Special Agent Application Portal are currently unavailable.”
“The FBI is aware of a cyber-criminal enterprise group claiming a compromise of the FBIJobs.gov portal and alleged impact to FBI employee personally identifiable information,” a spokesperson for the FBI told CNET via email. “While the point of breach is still undetermined — whether a third-party or the FBI’s enterprise — we are actively and aggressively investigating this matter and working closely with those third-party providers that support FBIJobs.gov to mitigate any and all risk.”
ShinyHunters has been linked to numerous ransomware attacks, including a breach of 4.4 million TransUnion credit records and access to servers belonging to Rockstar Games, the developer of the Grand Theft Auto series. The group usually demands extortion payments to prevent it from leaking the stolen information.
However, the attack on the FBI’s data is different and has potentially much more serious implications.
The group reportedly wants the FBI to correct what it calls false allegations in a Public Service Announcement that the FBI issued about it. The report notes that ShinyHunter “actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases swatting.”
In an email to The New York Times, a representative of ShinyHunters wrote, “We reiterate we are not extorting the FBI and this is not financially motivated… Our intention, goal and motive is to solely set the record straight.”
But the nature of the stolen data elevates this breach beyond corporate extortion.
Joseph Cox, who broke the story at 404 Media, wrote via email, “This data presents significant national security and counterintelligence risks, and isn’t in the hands of a foreign intelligence agency, but a group of likely younger, English-speaking hackers.”
A security analyst who asked to remain anonymous to avoid retaliation from the hacking group reiterated that this is a serious national security issue. “Remember, the FBI is tasked with both counterespionage and counterterrorism,” they said. “This could destroy [FBI employees’ ability] to go undercover, travel to other countries and more,” including threats to individuals and families.
Asked about the group’s claim that it has nothing to do with extortion, the analyst said, “Never trust anything they say. Ever.”
They said that advice also comes directly from colleagues who advise companies on how to handle the extortions. Gaining access to such sensitive data could be monetarily valuable to a state-level intelligence agency.
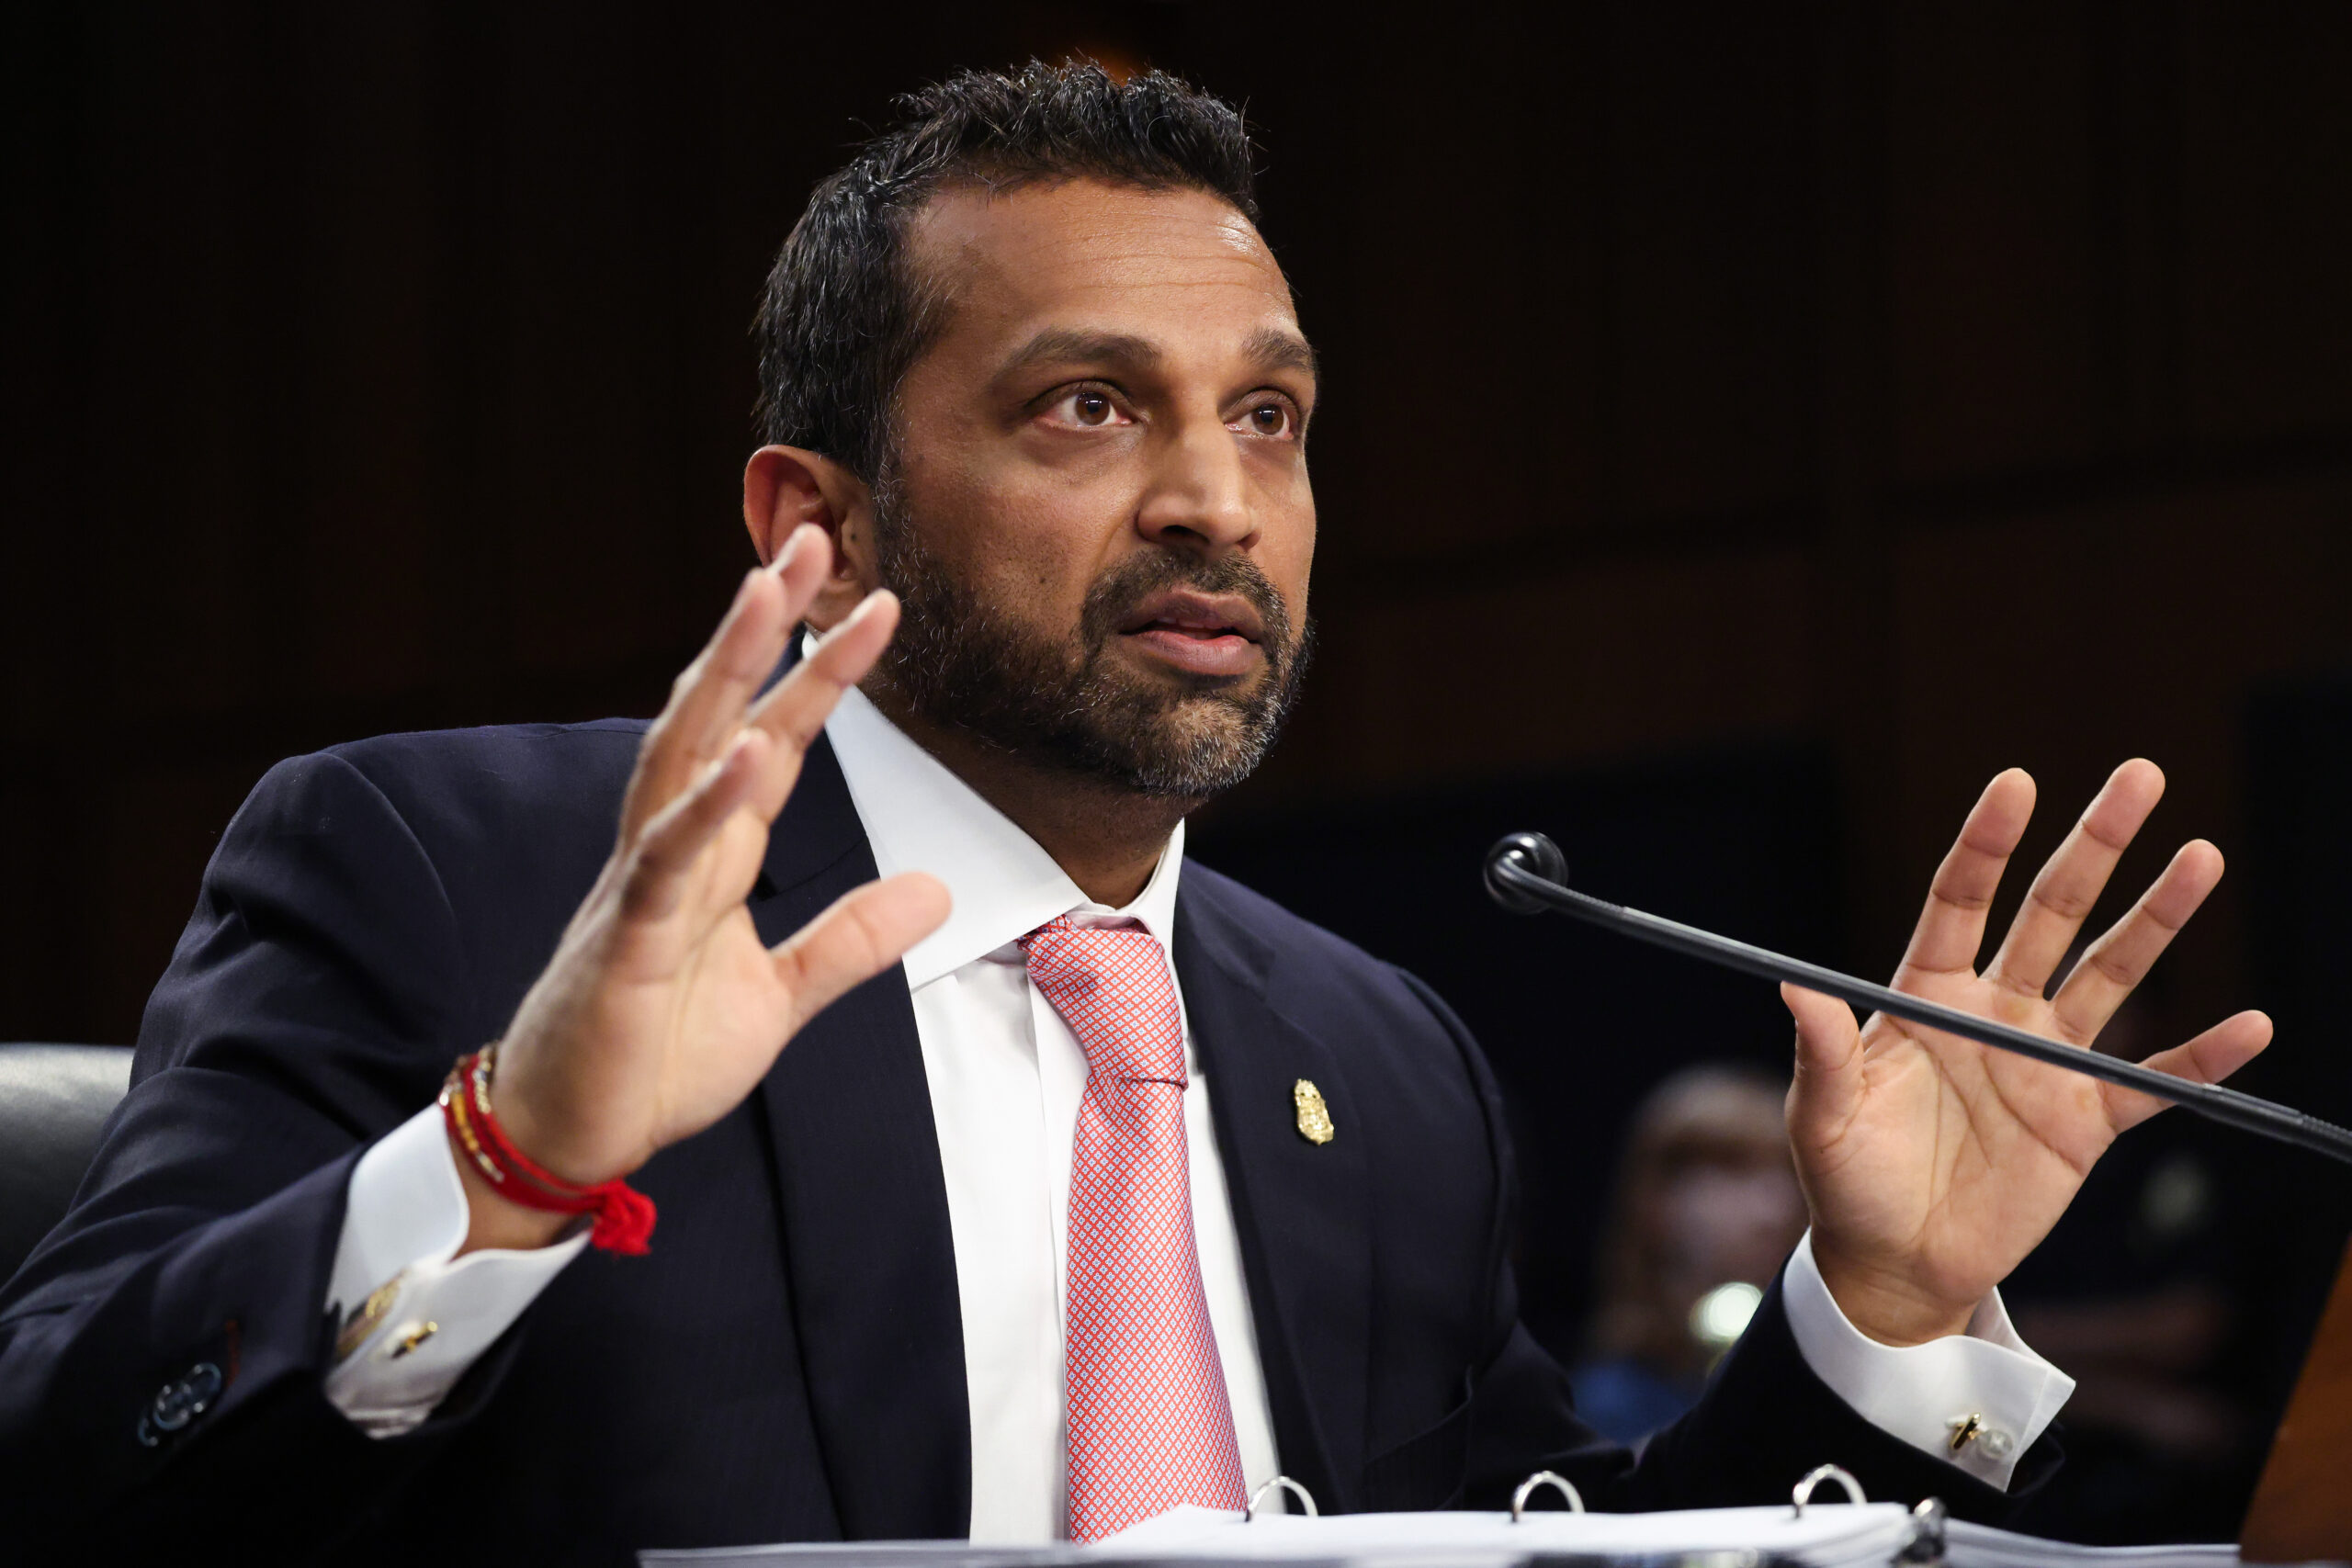
The FBI has seen other notable cyberattacks this year, including “suspicious activities” on the system the bureau uses to manage wiretapping and surveillance and claims by an Iran-backed group said to breach the personal email of FBI Director Kash Patel.

See full bio
Read the full article here